Autonomous Offensive Proof Packs: Moving Beyond Noise in DevSecOps
Static code scanners emit thousands of unvalidated warnings. Learn how PandaONE generates executable proof packs to prove exploitability in continuous CI/CD pipelines.
Your SAST job is green, but the ticket is still open because nobody could reproduce the SQLi warning on line 412. Static rules fire on syntax; they rarely prove a request actually reaches the sink in your running app.
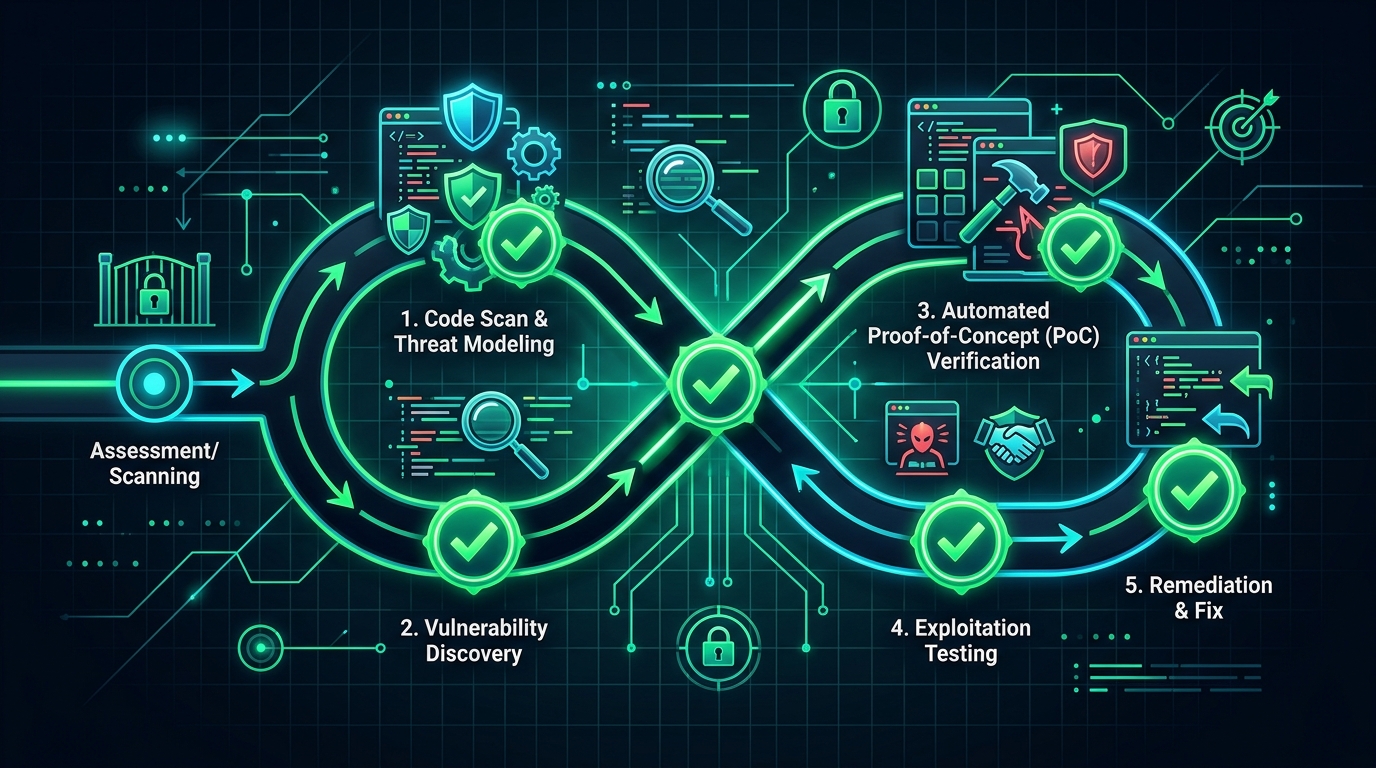
Proof Packs are PandaONE’s answer on the other side of that gap: after discovery, the worker attempts a safe, bounded exploit and saves the HTTP exchange (or equivalent evidence) so a developer can replay the issue locally.
Where static noise comes from
SAST and pattern DAST are cheap to run. They also:
- Cannot see whether tainted data reaches a live handler.
- Often miss middleware, gateways, and custom sanitizers.
- Push reproduction work onto humans already buried in PR alerts.
That is useful for hygiene. It is a poor sole signal for “ship or block.”
What a Proof Pack contains
When validation succeeds, you get material you can paste into a terminal or ticket:
- Proof vector — headers, body, and response that show the issue is reachable.
- Reproduction steps — usually a curl command or short script, not a PDF page reference.
- Remediation context — enough detail to patch and re-run the same proof on the branch.
Runs are scoped to authorized targets (verified domains, attested mobile builds, repos you connected). They are designed to be non-destructive; they still exercise real endpoints, so scope matters.
SAST/DAST vs proof validation
| Typical SAST/DAST export | Proof Pack | |
|---|---|---|
| Signal | Pattern or rule ID | Replayable request/response |
| False positives | Common; triage-heavy | Issues without proof do not ship |
| Developer artifact | Spreadsheet or PDF | curl + evidence bundle |
| CI fit | Often advisory | Gate on confirmed critical proofs when you configure it |
Exact CI wiring depends on your pipeline — API keys, webhooks, and fail policies live in platform docs.
Using proofs in DevSecOps
Practical pattern:
- Let static tools run wide on every commit (fast, noisy).
- Run offensive validation on merge candidates or nightly against a staging URL you verified.
- Block only on findings that include a proof pack you can replay.
- Re-run the same proof after the fix merges.
That keeps velocity on small diffs while keeping “exploitable right now” a higher bar than “rule matched once.”
For the product loop (Finalizer, categories, no raw tool names), see proof-backed findings. To try it on your stack, start from platform documentation.
